
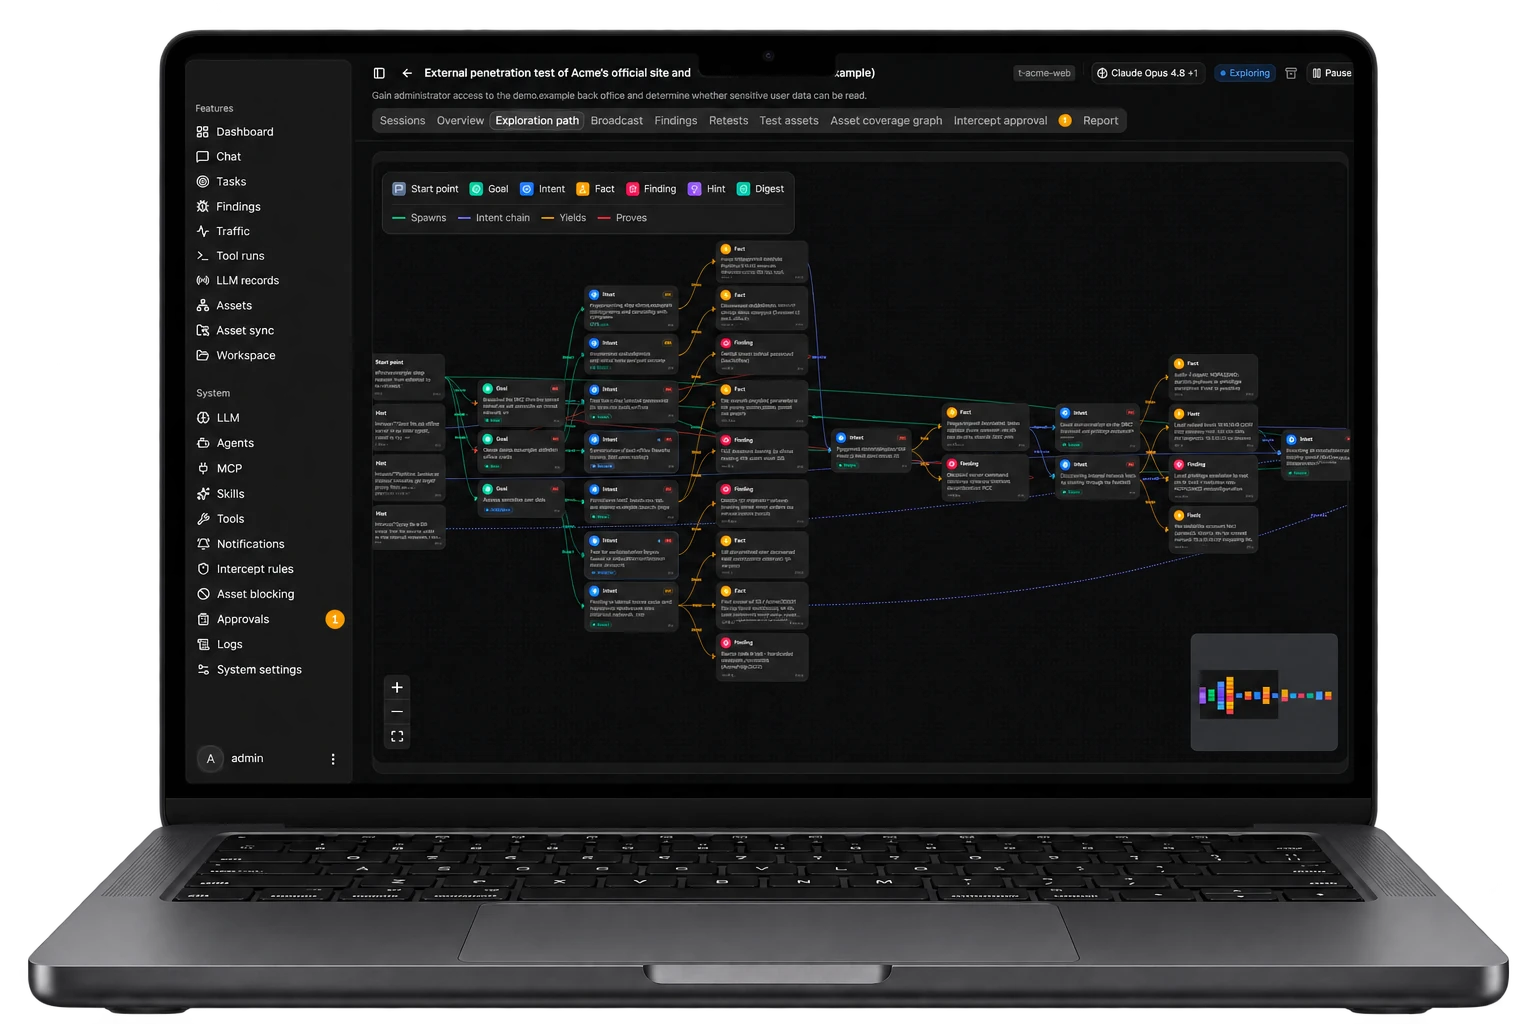
AI stronger than real hackersattacks your services
AI attacks within the agreed scope and shows where attackers get in, what they can take and what to fix first.
One free test per company
Your application has been received.

Sound familiar?
Clients ask about security
and we cannot answerNo dedicated staff
and no idea where to start
Worried customer data
could leakTest quotes are
too expensive
Redzone solves this
- 1
AI attacks
Multiple AI agents with separate roles work at once and try every path from entry to data.
- 2
You fix
We report what to fix and in what order, ready to hand to your engineers or vendor.
- 3
AI confirms
After the fix, we confirm the same path is closed.
Not just a list of holes
You see how to fix them
Find the holes in your services for free
Register for the free testWhy Redzone
AI models and systems
stronger than real hackers
We use the latest AI models built for attack work. Multiple agents with separate roles run at once and test far more paths than a person trying them one by one.
See the holes and
the data at risk
We report the entry point, how privileges were raised and what data was reached, along with the steps to reproduce it.
Hand over what to fix
and in what order
The report goes straight to your engineers or vendor. After the fix, we confirm the same path is closed.
The first test costs nothing
Register for the free testWhat we cover
From websites to native apps, APIs and cloud, we follow the path from entry to data in the same order as a real attack.
We look for ways in through public sites, forms and member screens.
We test iPhone, Android, Windows and Mac apps and the traffic behind them.
We test the APIs your apps connect to and internal systems reachable from outside.
We check for settings and storage left open to the outside.
We report what to fix and in what order, then retest after the fix.
Start with a free test
Register for the free testHow we differ
People testing one path at a time
Many paths tested at once
A person tries one path after another. Multiple AI agents run together and cover combinations people cannot get to.
Scanners that list weaknesses
See the path that actually worked
A list of weaknesses does not show whether you can really be breached. We report the path from entry to data.
Tests that end with a report
We confirm the fix worked
We tell you what to fix and in what order, then confirm the same path is closed.
See how attackers would get in
Register for the free testHow it works
Apply
Tell us your company and target domain.
Confirm ownership
We confirm the domain belongs to you.
Agree on scope
We explain the scope and points to note, then agree.
Run the test
Multiple AI agents attack within the agreed scope.
Report and retest
We report the results and retest after your fix.
We only test the agreed scope
FAQ
How is this different from a test by human hackers?
Multiple AI agents with separate roles try many paths at the same time. The report shows the paths that worked and how to reproduce them.
What do I do with the report?
Pass it to your engineers or vendor. It shows what to fix and in what order. After the fix, we confirm the same path is closed.
Does the test start as soon as I apply?
We start after confirming domain ownership and agreeing on scope.
Will my service go down during the test?
No. We agree on a scope and method that keep it running before we start.
Is there a cost?
One test per company is free.